
Pentagon Data Leak Exposes Personal Records of Nearly 3 Million Military and Civilian Personnel
A major cybersecurity breach at the Defense Manpower Data Center exposed unencrypted Social Security numbers and job details of over 3 million living and deceased military personnel.
 Rajeev
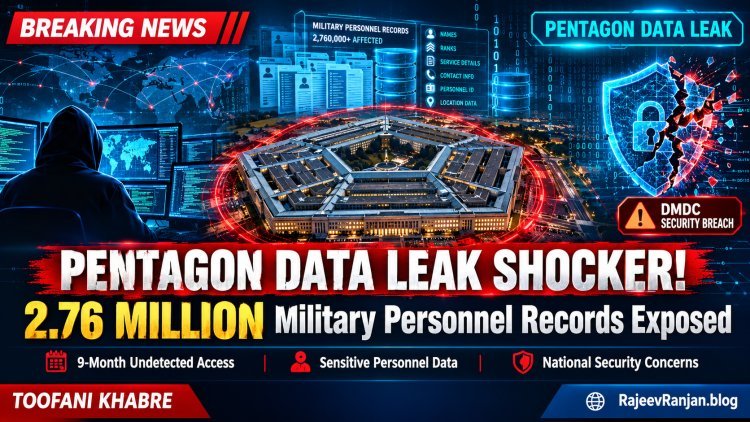

Pentagon HR Breach Exposes Unencrypted Data of Over 3 Million Personnel
WASHINGTON — In one of the most severe national security vulnerabilities to strike the U.S. Department of Defense in recent years, a massive data breach at the Defense Manpower Data Center (DMDC) has exposed the personally identifiable information (PII) of more than three million military and civilian personnel.
According to defense officials, unauthorized users gained access to a core DMDC information system holding critical human resources and entitlement data.
Scope of the Compromised Data
Official disclosures confirm the intrusion impacted approximately 2.76 million living individuals and roughly 294,000 deceased persons associated with the armed services and civilian defense enterprise.
The compromised records contained critical personal and career information, including:
-
Social Security numbers (SSNs)
-
Military Occupational Specialty (MOS) codes and job roles
-
Full names, dates of birth, and contact information
-
Demographic details and service history tracking
Alarmingly, internal review notifications confirmed the exposed data was stored without encryption, greatly simplifying extraction and analysis by unauthorized parties once inside the network.
National Security and Counterintelligence Risks
Cybersecurity and intelligence experts warn that the exposure of military occupational roles paired with personal identifiers creates an exceptional counterintelligence hazard.
"If a foreign adversary acquires this level of structured career and personal data, it opens the door to targeted spear-phishing, long-term intelligence approaches, and potential extortion," warned a national security analyst reviewing the incident disclosures.
Response and Ongoing Remediation
The Defense Manpower Data Center patched the file-sharing vulnerability immediately upon discovery on July 16, 2026. A broader "cyber hunt" operation led by the Defense Information Systems Agency (DISA) is currently underway to assess whether adversaries maintained persistent access or exfiltrated additional systems.
To mitigate immediate harms to service members and federal workers:
-
Notification Letters: Affected current and former personnel are receiving official breach notices detailing their specific risk exposure.
-
Credit Monitoring Services: The Department of Defense is providing one year of free credit monitoring and identity-restoration services through security vendor IDX.
-
Internal Audit: Systemic architectural reviews are being deployed across all active personnel databases managed by the DoD.
Pentagon officials maintain that there is currently no direct evidence that the exposed records have been published or sold on dark web markets, though risk evaluations remain active.